

The federal cybersecurity agency released its election infrastructure security plan on Thursday, roughly five weeks before midterm elections scheduled for Nov. 3.
What is in the document?
Thirteen pages outlining potential threats to voting systems and listing services the Cybersecurity and Infrastructure Security Agency offers state and local election officials at no cost. The document states that election security is not a partisan issue and frames it as a matter of national security. It was produced at the direction of the Homeland Security secretary, who assigned the task in July.
Was it late?
Yes. The secretary had initially said the plan would be published by mid August. A document intended to help officials prepare arriving in late September gives states less time to act on it before ballots begin moving, though most election security work at the state level runs on a longer cycle than any single federal document.
What can the federal agency actually do?
Less than many voters assume, and this is the part worth understanding. Elections in the United States are administered by states and counties, not by the federal government. The agency created in 2018 within the Department of Homeland Security provides voluntary services, including vulnerability scanning, penetration testing, physical security assessments and threat information sharing. It does not run elections, certify equipment or compel any jurisdiction to accept help. Election infrastructure security at the operational level is a state and county responsibility.
Why does that structure exist?
Deliberate design. Decentralised administration means there is no single system to compromise nationally, which is a genuine security advantage. The tradeoff is uneven capability, since a large county with a dedicated IT staff and a rural county with one part time clerk face the same threats with very different resources. Voluntary federal services exist to narrow that gap, and their effectiveness depends entirely on uptake.
What threats are officials watching?
The agency has previously warned states about foreign threats, including concerns raised this year about voting equipment containing foreign manufactured components. Broader categories in this area typically include attempts to access voter registration databases, disruption of results reporting websites, ransomware against county systems and physical threats to election workers. The presence of a threat category in a planning document does not indicate an incident has occurred.
Should voters be worried?
Concerned enough to verify, not enough to disengage. No federal agency has reported a compromise affecting vote counts in recent elections, and paper records combined with post election audits provide a check that purely electronic systems would not. The more common practical problems voters encounter are registration issues and polling place changes rather than anything involving election infrastructure security.
What can a voter actually do?
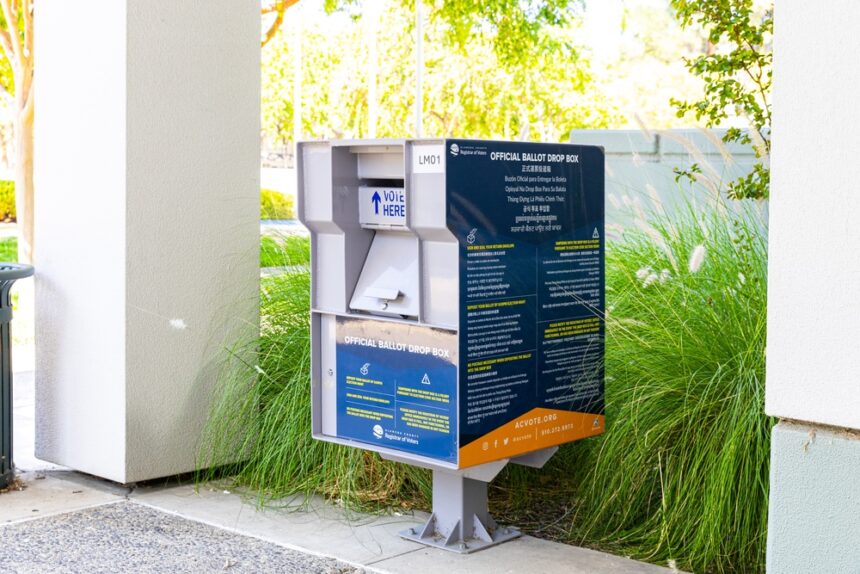
Check registration status and polling location directly through your state or county election office rather than through third party sites, confirm any mail ballot deadlines well before they arrive, and treat claims circulating on social media about equipment or results with the same scepticism you would apply to any unsourced assertion. Local election offices answer questions from the public and are the authoritative source for your own jurisdiction.
What happens next?
States decide what to use. The plan is guidance and an offer of services, not a requirement, and its practical effect will be visible only in how many jurisdictions take up what is available before November.